01
Use the real caller Origin
Enter the frontend's scheme, host and port, not the API URL. The local CORS checker compares that exact Origin with the pasted Allow-Origin field; the browser mode instead uses this site's fixed Origin.
HTTP / Request Debugging
Paste actual and optional OPTIONS response headers, or explicitly run a browser GET from this page.
Pasted headers stay in this browser. Local analysis sends no request.
Paste response headers to begin.
This Origin is for local analysis only. Browser GET uses this page's actual Origin.
Paste response headers to begin.
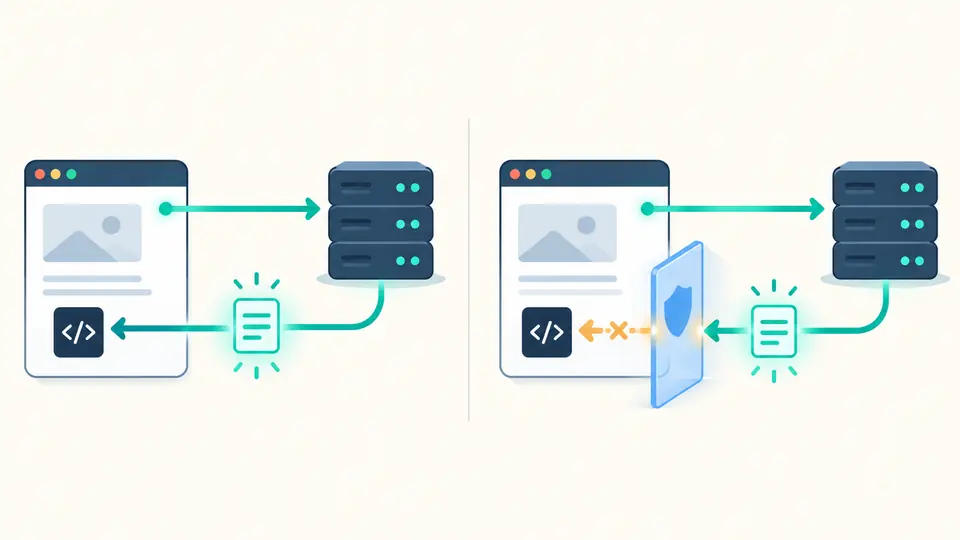
Your server logs show a 200 response, but fetch still rejects it. The CORS tester separates the HTTP exchange from the browser's decision to expose that response to JavaScript.
Start with headers copied from DevTools; no request is sent. Use the CORS checker conditions for the Origin, method and request headers you actually need, then compare a separate preflight response if the browser would send OPTIONS.
A response reaching your server is only half the story.
A plain GET may reach the server and return HTTP 200 while the browser withholds it from JavaScript. This CORS tester checks the actual Access-Control-Allow-Origin value before it calls a response readable; it never treats server success as browser permission.
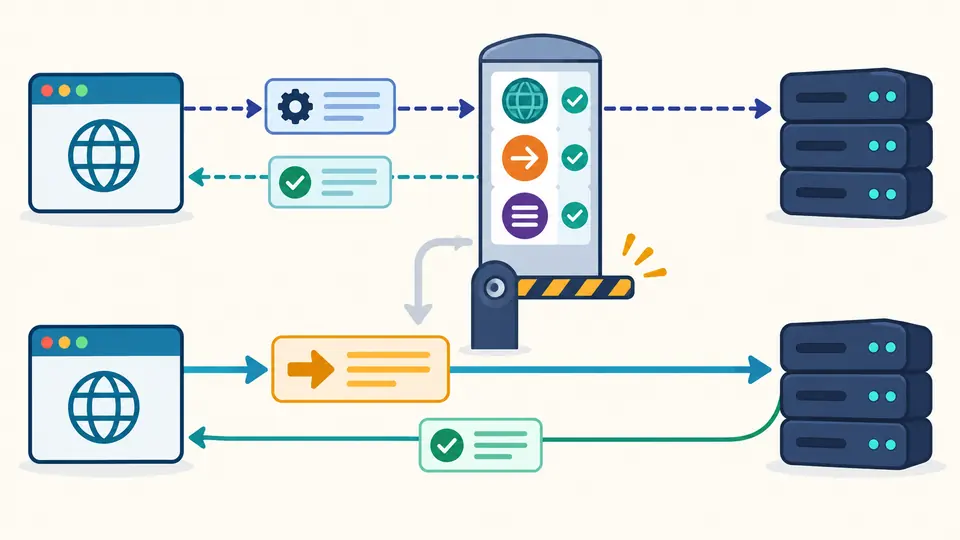
A JSON POST or Authorization header can trigger OPTIONS before the actual request. If you paste only the final response, the preflight remains unverified. Add the OPTIONS status and headers to see which method or request header was refused.
Enter the frontend's scheme, host and port, not the API URL. The local CORS checker compares that exact Origin with the pasted Allow-Origin field; the browser mode instead uses this site's fixed Origin.
JSON Content-Type, Authorization and non-simple methods can trigger preflight. Add only request header names; values are irrelevant to this classification. An empty OPTIONS box means the gate remains unverified.
A changed input immediately disables the old report. Auto analysis waits 350 ms; turn it off to use Analyze or Ctrl/Cmd + Enter. Browser GET is always manual and reports only what page script can observe.
Compare one Origin with the actual response. Wildcard Allow-Origin fails with credentials: include, and a specific Origin still needs Allow-Credentials: true. Authorization as a request header triggers its own preflight rule; it is not the credentials switch.
The CORS preflight tester checks the OPTIONS status, Allow-Methods and Allow-Headers against the selected method and required header names. It reports missing fields and names separately instead of collapsing every failure into one red badge.
Read Expose-Headers and Vary without inventing an endpoint test. A particular Allow-Origin may require Vary: Origin for caches, but one copied response cannot establish whether a server reflects every Origin.
Only an explicit click sends a credential-free GET from this page's actual Origin. A readable HTTP error still proves the browser exposed that response. When fetch rejects, this page cannot show the hidden status or headers.
The HTTP response can arrive while the browser refuses to expose it to page JavaScript. Check the actual Allow-Origin and credential fields; for a non-simple request, also check the separate OPTIONS response. A server log or curl success alone is insufficient.
A simple GET can be sent directly, followed by a response read check. JSON POST, non-simple methods or custom headers first need a successful OPTIONS exchange authorizing the Origin, method and header names. The actual response still needs its own Allow-Origin check.
The default local CORS tester analyzes pasted text in your browser and sends no request. Browser GET is a separate, explicit mode: clicking Run sends a GET to the URL from this page, without credentials or custom headers.
CORS governs what browser JavaScript may read. It does not replace authentication, authorization or server-side validation; non-browser clients do not enforce the browser's CORS read restriction.
A credentialed cross-origin response requires a specific matching Origin and Access-Control-Allow-Credentials: true. The browser rejects a wildcard Allow-Origin for this mode. The local analyzer flags that combination in actual and preflight responses.
Need another scenario explained?
Copy the actual and, where needed, OPTIONS headers from DevTools. The CORS tester keeps the two decisions separate before you change server configuration.
Local analysis by default; browser GET only after your click.