01
Choose a public target
A bare domain gains HTTPS automatically. The example fills the URL but does not send a request; clicking Check headers is what contacts the target.
HTTP & Request Debugging
Check the first response from a public URL
Enter a public URL, then run a check.
The URL goes to our Worker, which requests the public site without your cookies or authorization. The target sees the request.
Enter a public URL, then run a check.
Use an HTTP header checker when a release seems live but a cache still serves an old version, or a redirect hides the response you meant to inspect. The report records the first hop at one point in time; you can check HTTP headers online without opening the destination.
This response headers checker starts with HEAD, falls back to GET only if HEAD is refused, and never follows Location. You can compare the values with a browser trace without treating a presence badge as a security verdict.
Observe the first response, then decide what to inspect next
A 301 or 302 is itself a response. The HTTP header checker retains its status and Location rather than silently showing the destination. That makes a misplaced redirect rule easier to spot.
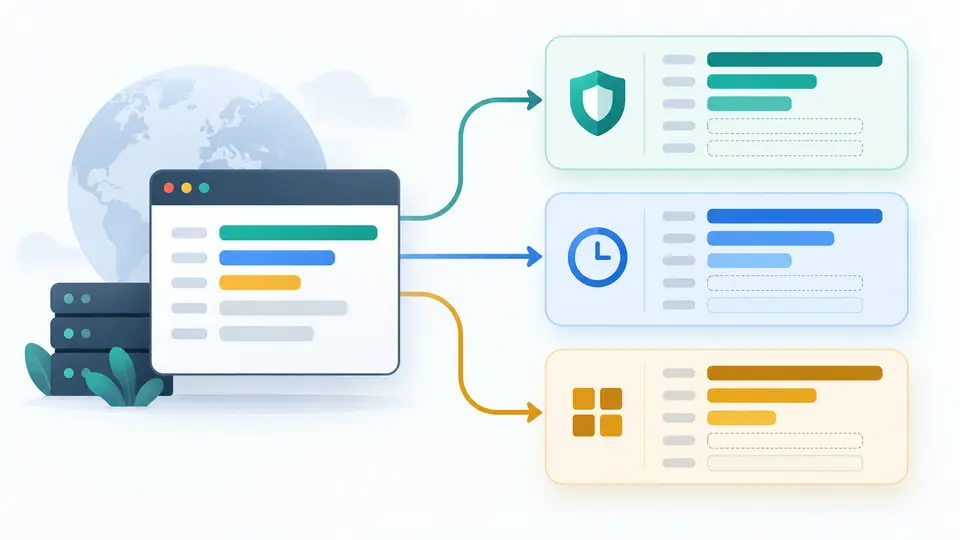
Security headers and cache headers appear in separate groups, with every other returned field retained. A missing label means only that it was not seen in this anonymous response; it is not a security score.
A bare domain gains HTTPS automatically. The example fills the URL but does not send a request; clicking Check headers is what contacts the target.
The checker tries HEAD first. A 405 or 501 triggers one GET fallback with the body discarded. A 3xx remains visible with its Location rather than opening the destination.
The time belongs to this check, not to the target’s Date header. Changing the URL makes the report stale and disables copy and download until another check succeeds.
A 4xx or 5xx response still has useful headers and is shown as a valid response. The report identifies HEAD or GET, plus the fallback when it happened.
Inspect CSP, HSTS, Referrer-Policy and related security headers as returned. The checker lists absent common fields without guessing whether a site is vulnerable.
Cache-Control, ETag, Vary and other cache headers stay beside their exact values. Compare a proxy or CDN response with the origin behavior you expect.
It requests the first response for one public URL and displays status, checked time and all returned header values. It groups common cache and security fields for easier inspection.
They can tell browsers how to handle content, transport and framing. The HTTP header checker shows observed values only; a present name does not prove that its policy is appropriate.
No. It shows the first 3xx and its Location without following it. Use a dedicated redirect checker to inspect subsequent hops.
A server may omit them on this path or for anonymous HEAD requests, or a CDN may change them. The report says only what this check observed.
The Worker sends an anonymous request from a different network. Vary, geographic routing, cookies, method and caches can change the response; compare the method and time first.
Still have a question?
Check one public response now, then save the exact header values with its timestamp.